
Always on
AI Security Engineer.
OpenHack finds and fixes vulnerabilities in your code, runs AI pentests, and prioritizes findings using real exploitability and business context like a real security engineer.
Trusted by leading engineering teams.
Book a demo
 Docura Health

- 01
Uncover the hardest logic-based vulnerabilities that traditional tools miss using the advanced OpenHack harness
- 02
Save 100+ hours with near zero false positives through auto-verification
- 03
Know what to fix first with intelligent prioritization based on
CVSS Scorestrue business impact - 04
Pentest every day, not once a year, with always-on AI pentesting
The most context-aware AI Security Engineer that works 24/7
Get startedFind, verify, and fix real vulnerabilities using AI.
102
export default function handler(req, res) {103
// Get the session104
const session = getServerSession(req, res, authOptions);+
const session = await getServerSession(req, res, authOptions);105
if (!session) {106
return res.status(401).json({ message: "Unauthorized" });107
}109
return tusServer.handle(req, res);110
}pages/api/file/tus/[[...file]].tsMissing await bypasses upload authentication
CVE-2026-36755Supply Chain Security
Secret Scanning
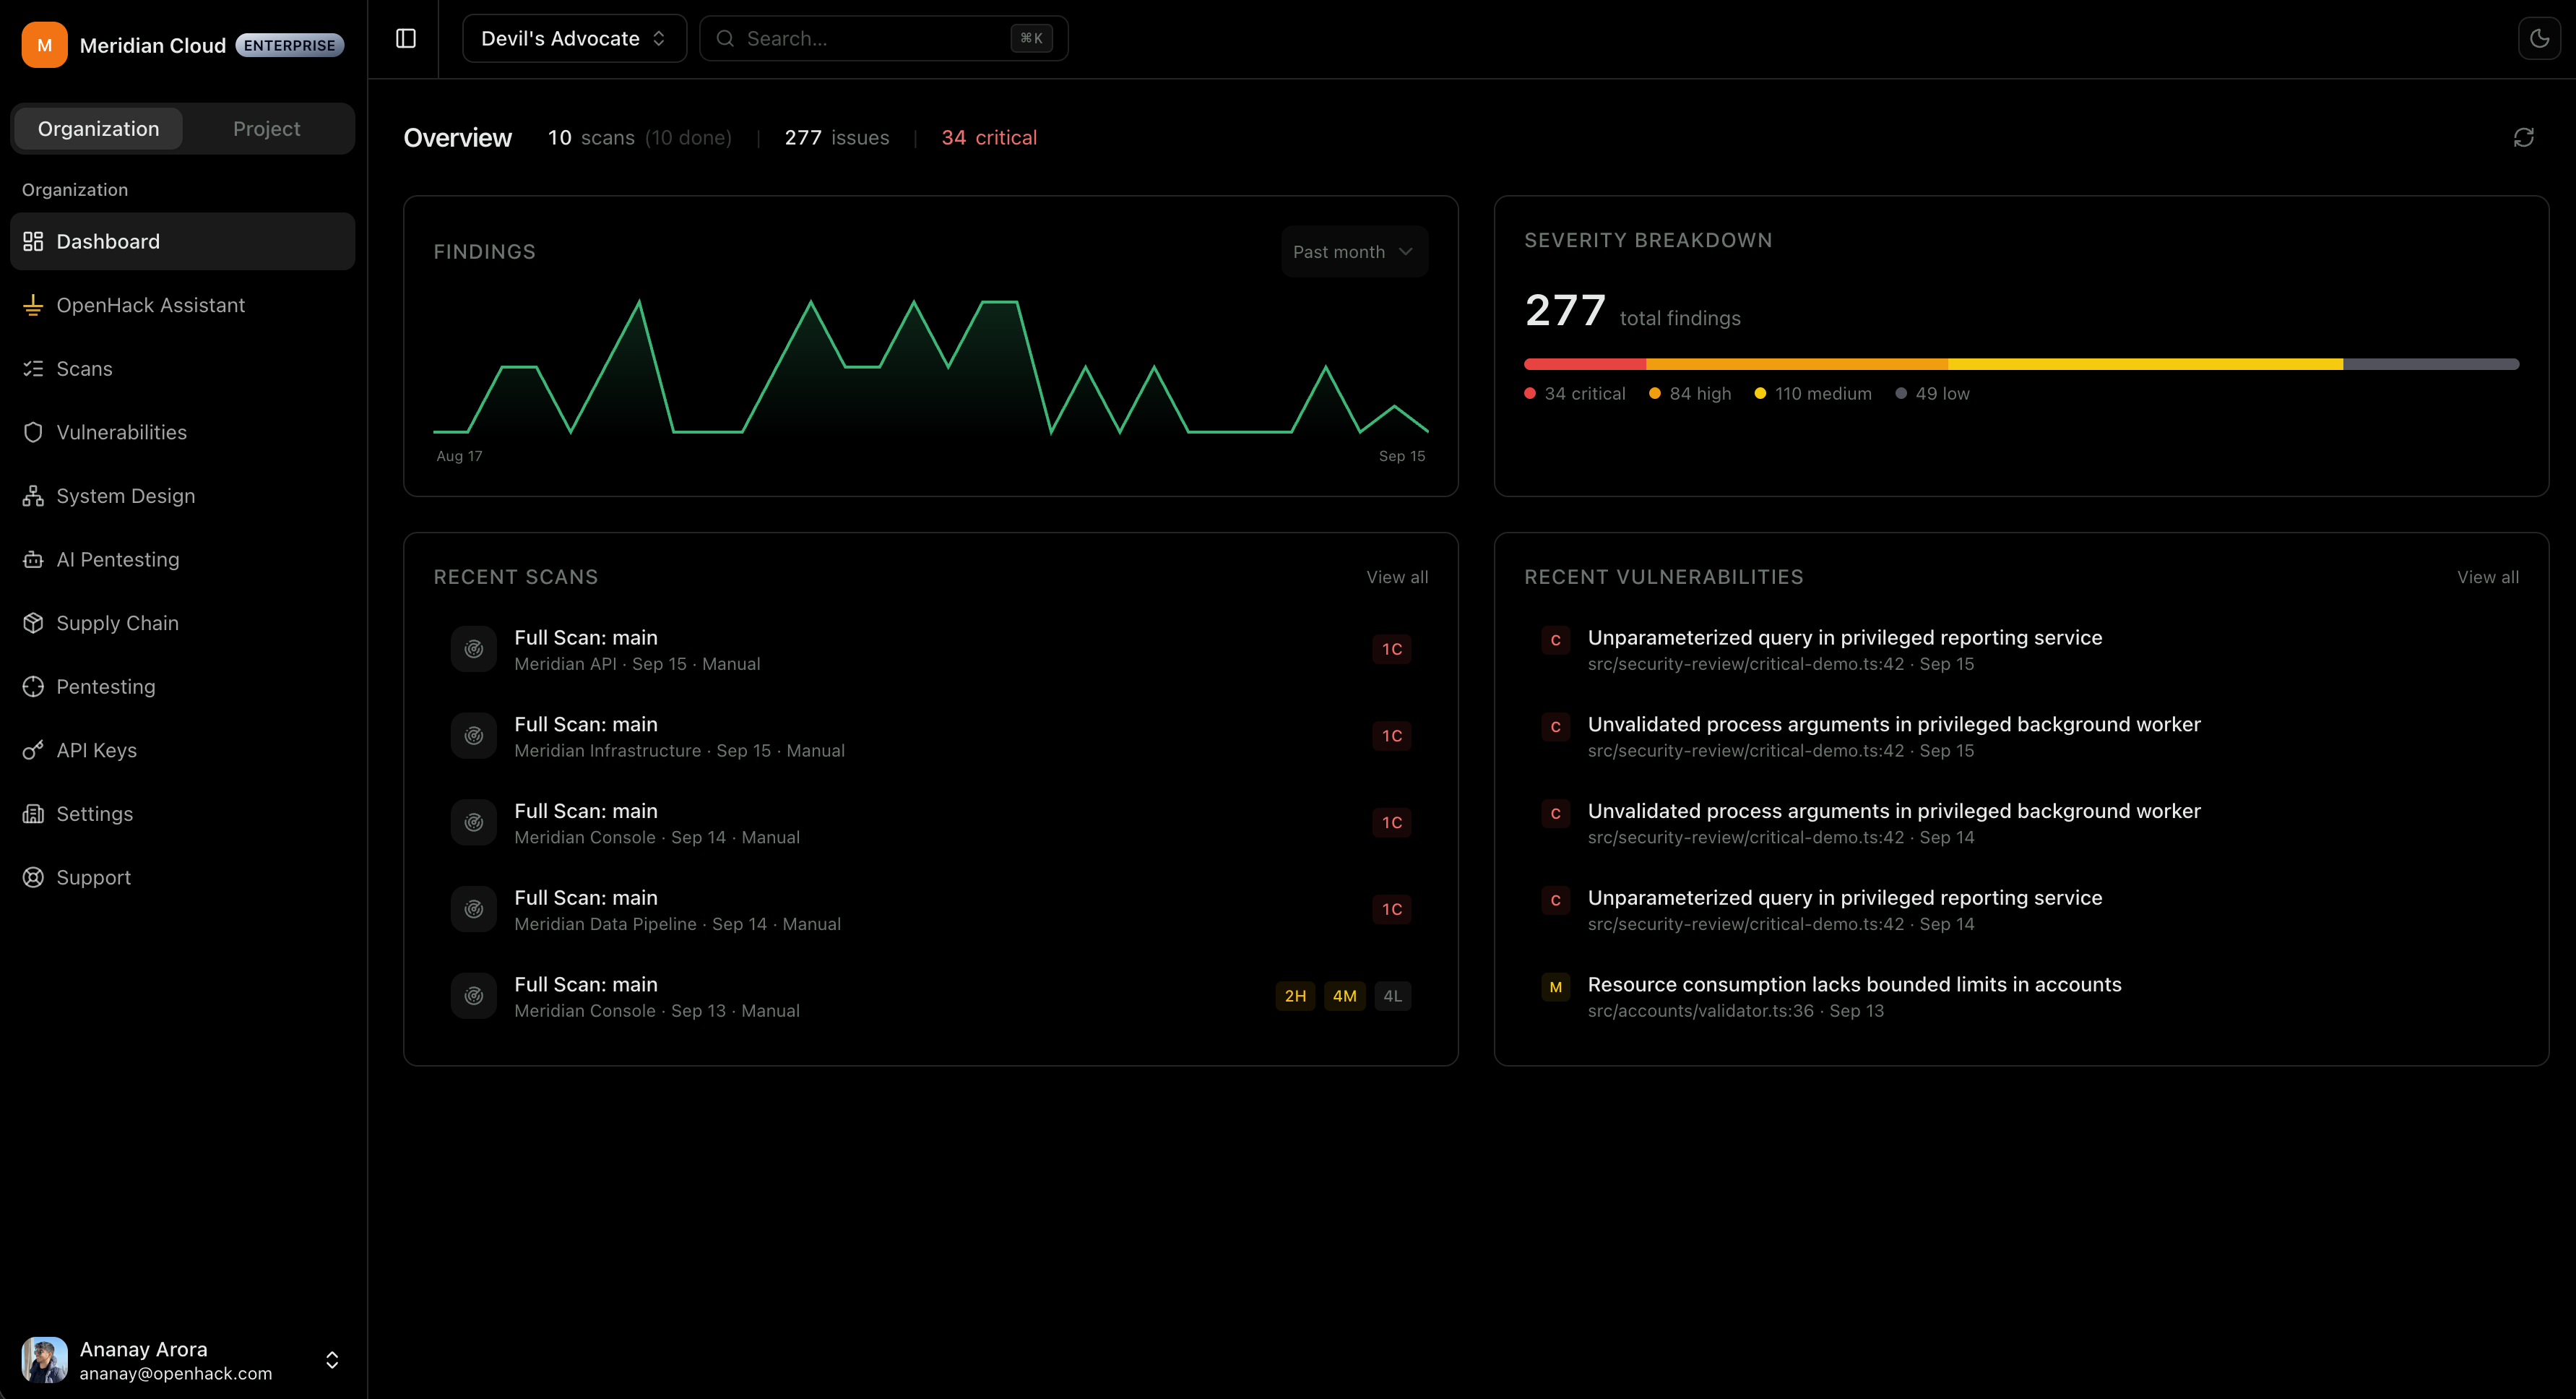
Auto prioritize vulnerabilities based on business impact
AI Vulnerability ManagementIntegrates with your stack
Slack
Tag @OpenHack. Get answers, right where your team works.
Linear
Assign it to OpenHack. Get a fix back as a pull request.
Security that grows with your team.
For Startups
Ship fast without making security a second job. Find and fix vulnerabilities, run pentests, and get ready for enterprise security reviews.
For Enterprises
Bring code scanning, pentesting, and vulnerability management into one workflow. Prioritize real business risk and give every team a clear path to remediation.
Frequently asked questions
What is OpenHack?
OpenHack is your Always on AI Security Engineer. It finds, verifies, prioritizes, and fixes vulnerabilities across your codebases and live applications.
What does OpenHack do?
OpenHack scans code, runs autonomous pentests, validates findings with working exploits, prioritizes them using real business impact, and prepares fix pull requests. It works across application code, authentication flows, APIs, dependencies, secrets, and business logic.
How does OpenHack verify vulnerabilities?
OpenHack validates findings by building a working proof of concept and reproducing the issue in a sandbox or browser before it reports the vulnerability.
What kinds of vulnerabilities can OpenHack find?
Beyond basic vulnerabilities, OpenHack finds business logic flaws, race conditions, timing attacks, IDORs, authentication bypasses, exposed secrets, and vulnerable dependencies. More importantly, it reasons across findings and intelligently chains vulnerabilities to demonstrate attack paths that isolated checks miss, like a real security engineer.
What AI models can I use?
You can use any AI model you want in the CLI and connect any provider. The platform uses OpenHack's managed zero data retention inference.
What is the difference between the open-source CLI and the platform?
The open-source CLI runs locally and gives you direct control over scans and models. The managed platform adds continuous scanning across repositories, team controls, business-aware prioritization, and fix pull requests.
Where is my data stored?
Your code, scan data, and findings are stored locally. Only requests needed for inference leave your environment, and all inference is processed within your local geographic region or data domicile.